> For the complete documentation index, see [llms.txt](https://docs.snyk.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.snyk.io/scan-fix-and-prevent/scan-with-snyk/snyk-api-web/getting-started-with-snyk-api-web.md).
# Getting started with Snyk API & Web
How to get started with Snyk API & Web dynamic application security testing
{% hint style="info" %}
**Snyk is rolling out a new navigation.** The steps on this page describe the classic interface. If your view looks different, visit [Navigate the Snyk Web UI](https://docs.snyk.io/navigate-the-snyk-web-ui#where-things-moved) to map these options to the new interface.
{% endhint %}
## Getting started with Snyk API & Web
Learn how to start scanning web applications for security vulnerabilities using Snyk API & Web.
### Overview
This guide walks you through the essential steps to begin using Snyk API & Web for security scanning:
1. Sign up for Snyk API & Web
2. Complete the onboarding flow
3. Review scan coverage
4. Analyze findings
### Sign up for Snyk API & Web
Create your account in Snyk API & Web to start scanning:
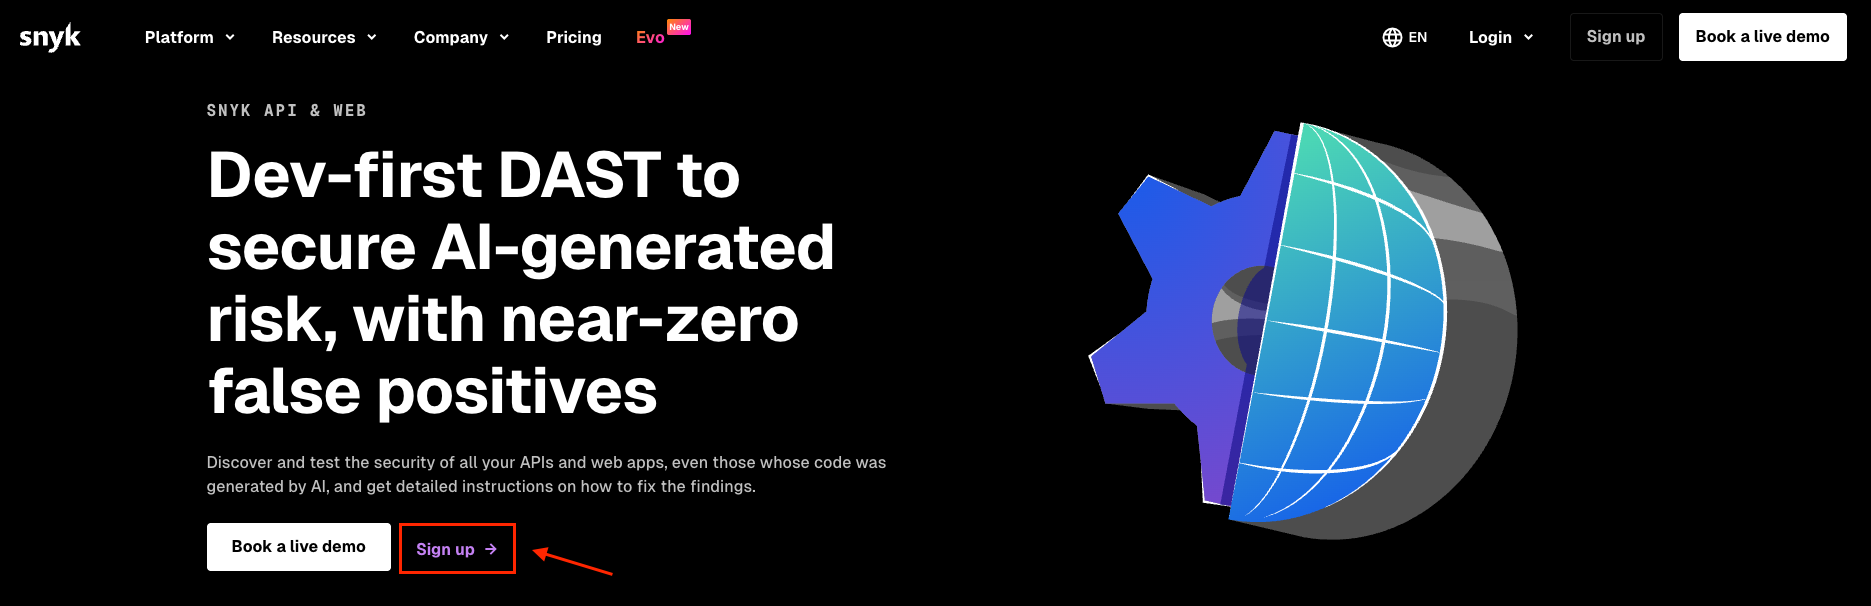
1. Navigate to and click **Sign up**.
2. Enter your email address and click **Submit**.
3. Check your email for a verification message and click **Verify email**.
4. Complete the registration form and click **Create account**.
### Complete the onboarding flow
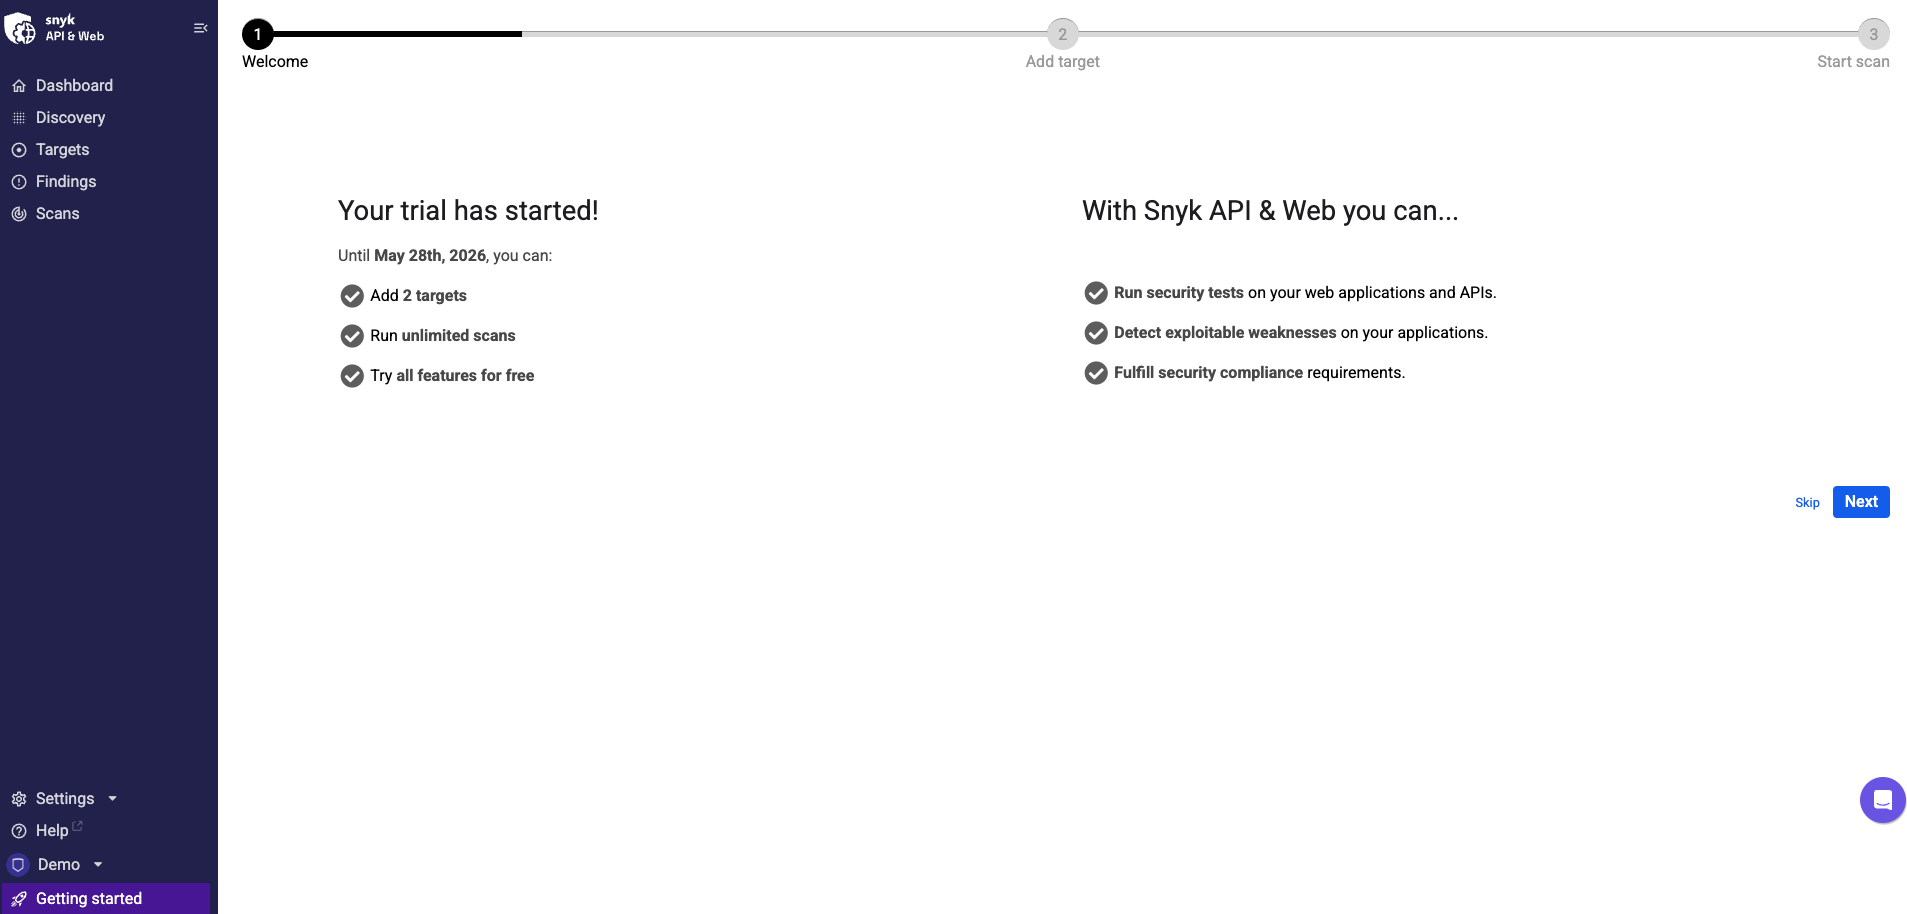
After creating your account, Snyk displays [best practices for deploying dynamic application security testing (DAST)](/scan-fix-and-prevent/scan-with-snyk/snyk-api-web/getting-started-with-snyk-api-web/best-practices-for-deploying-dast.md) and guides you through the initial setup:
1. Click **Next** to begin.
2. Select **My own target** and click **Next**.
3. Select **Web** as the target type and click **Next**.
4. Add your first target:
* **Target name**: Enter a descriptive name (for example, "Example")
* **Target URL**: Enter the URL to scan (for example, `https://example.com`)
5. When you add a target, Snyk verifies that you own the domain. Snyk performs extensive security tests that can appear as malicious attacks. Domain verification proves that you own the domain and are authorized to run security tests.
1. The onboarding flow automatically verifies ownership when possible. If automatic verification is not available, you must prove ownership manually through the guided process. Alternatively, you can install a scanning agent to reach internal targets. For more information, see how to [verify domain ownership](/scan-fix-and-prevent/scan-with-snyk/snyk-api-web/configure-targets/verify-domain-ownership.md) and [how to install a scanning agent](/scan-fix-and-prevent/scan-with-snyk/snyk-api-web/start-scanning/overview-scanning-agent/install-scanning-agent.md).
6. Click **Next** after configuring domain verification or the scanning agent.
7. Click **Scan** to start scanning your target.
8. A success page confirms that your scan started.
### Review scan coverage
The **Scan Overview** page shows the progress of your scan.
While the scan runs, you can download the preliminary crawling report to review coverage so far. Then, after the scan completes, download the full crawling report.
Amongst other information, the **crawling report** shows, for each URL discovered, the **HTTP request method** and **response codes**, whether the request was **authenticated** or not, whether the endpoint was sent to the scanner for **further tests** or simply **crawled**, and why.
Use this information to verify that the scanner reached all intended parts of your application and identify any access issues.
### Analyze findings
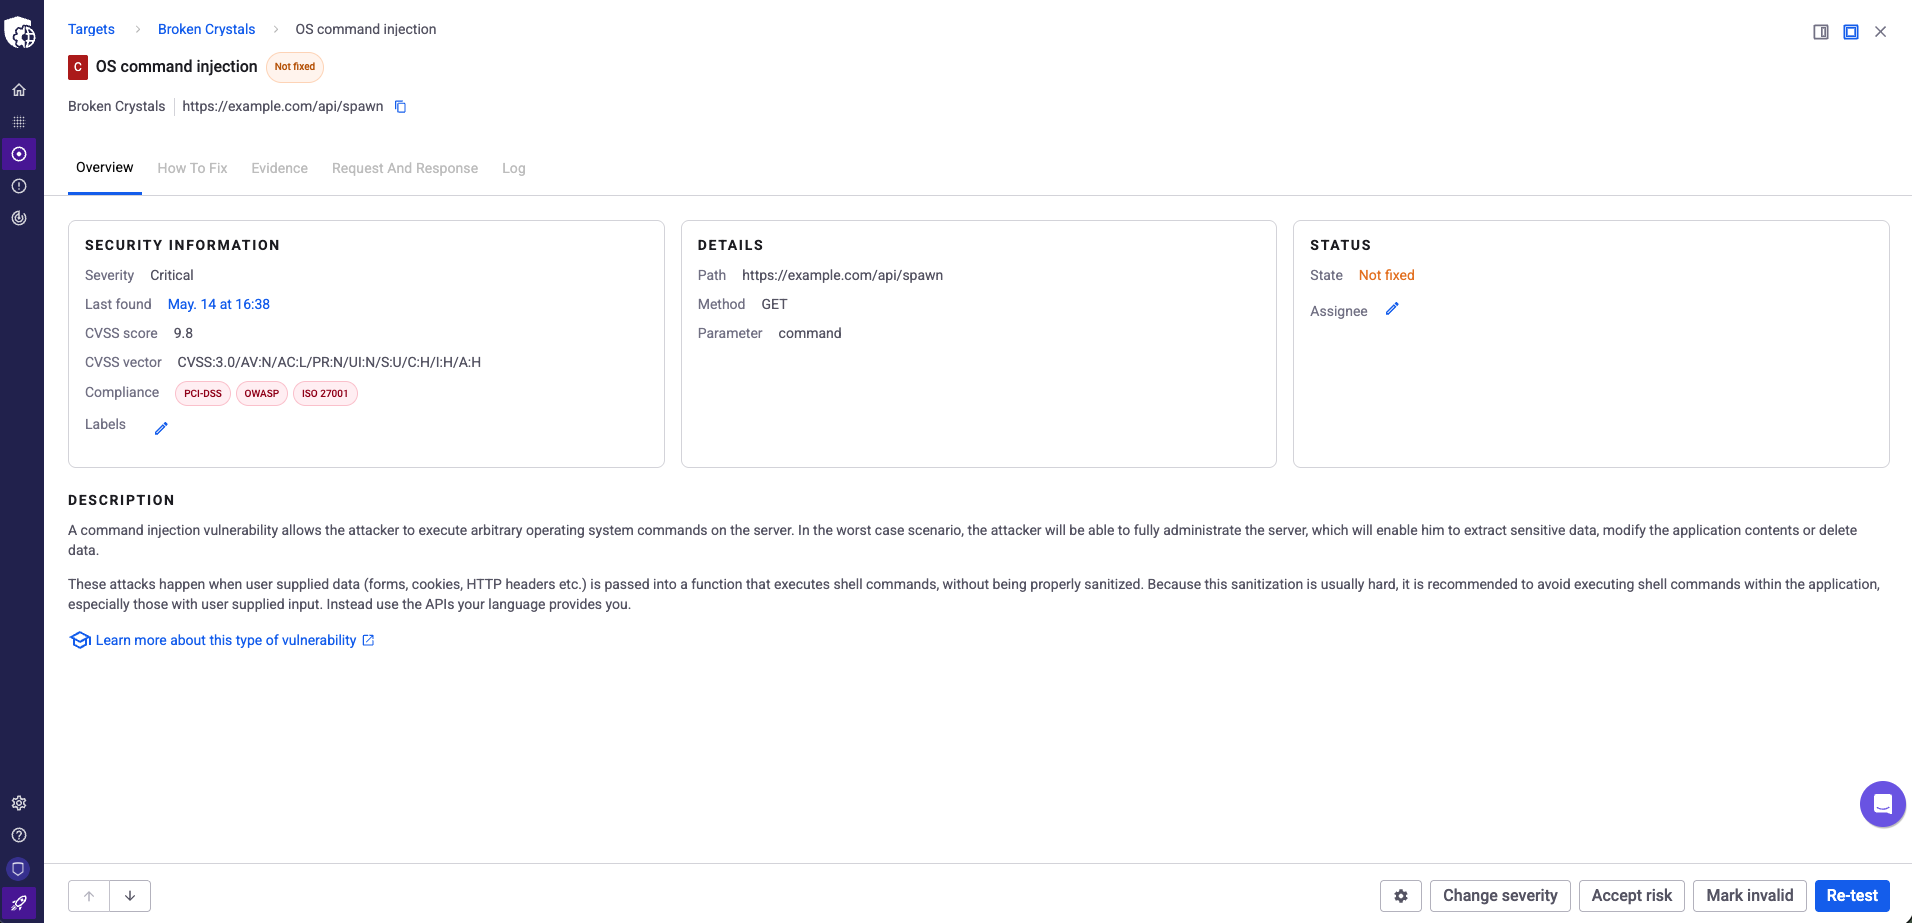
The **Scan Findings** page displays all security vulnerabilities identified during the scan.
Click a finding in the findings list to view its CVSS score, vulnerability description, remediation guidance, and additional context.
This information helps you understand the severity and impact of each vulnerability so you can prioritize and plan remediation work.
### Next steps
You can now scan applications, identify vulnerabilities, and plan security improvements.
To learn more:
* Review [best practices for deploying DAST](/scan-fix-and-prevent/scan-with-snyk/snyk-api-web/getting-started-with-snyk-api-web/best-practices-for-deploying-dast.md)
* Understand [when you can scan a production site](/scan-fix-and-prevent/scan-with-snyk/snyk-api-web/getting-started-with-snyk-api-web/can-i-scan-a-production-site.md)
* Understand [what is a target](/scan-fix-and-prevent/scan-with-snyk/snyk-api-web/configure-targets/what-is-a-target.md)
* Learn [how to configure and scan an API](/scan-fix-and-prevent/scan-with-snyk/snyk-api-web/configure-targets/configure-api-targets.md)
* Explore [how to configure authentication](/scan-fix-and-prevent/scan-with-snyk/snyk-api-web/configure-targets/configure-authentication.md)
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.snyk.io/scan-fix-and-prevent/scan-with-snyk/snyk-api-web/getting-started-with-snyk-api-web.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.