> For the complete documentation index, see [llms.txt](https://docs.snyk.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.snyk.io/platform-administration/user-management/single-sign-on-sso-for-authentication-to-snyk/custom-mapping/examples-setting-up-custom-mapping-for-idps/example-setting-up-custom-mapping-for-an-okta-oidc-app.md).
# Example: setting up custom mapping for an Okta OIDC app
Example of setting up a Snyk custom mapping integration for an Okta OIDC application
{% hint style="info" %}
**Snyk is rolling out a new navigation.** The steps on this page describe the classic interface. If your view looks different, visit [Navigate the Snyk Web UI](https://docs.snyk.io/navigate-the-snyk-web-ui#where-things-moved) to map these options to the new interface.
{% endhint %}
## Example: setting up custom mapping for an Okta OIDC app
Follow these steps to configure an integration for an Okta OIDC application.
You need permissions in Okta to create app integrations and to edit user profiles in the **Profile Editor**. Complete the [SSO information worksheet](/platform-administration/user-management/single-sign-on-sso-for-authentication-to-snyk/set-up-snyk-single-sign-on-sso.md#resources-for-sso-setup) for Okta before you start. Snyk turns on custom mapping only after you finish the setup steps, so contact your Snyk account team or [Snyk Support](https://support.snyk.io) when you have finished. See [Custom mapping](/platform-administration/user-management/single-sign-on-sso-for-authentication-to-snyk/custom-mapping.md) for the requirements and the role assertion format.
### Create an Okta OIDC app
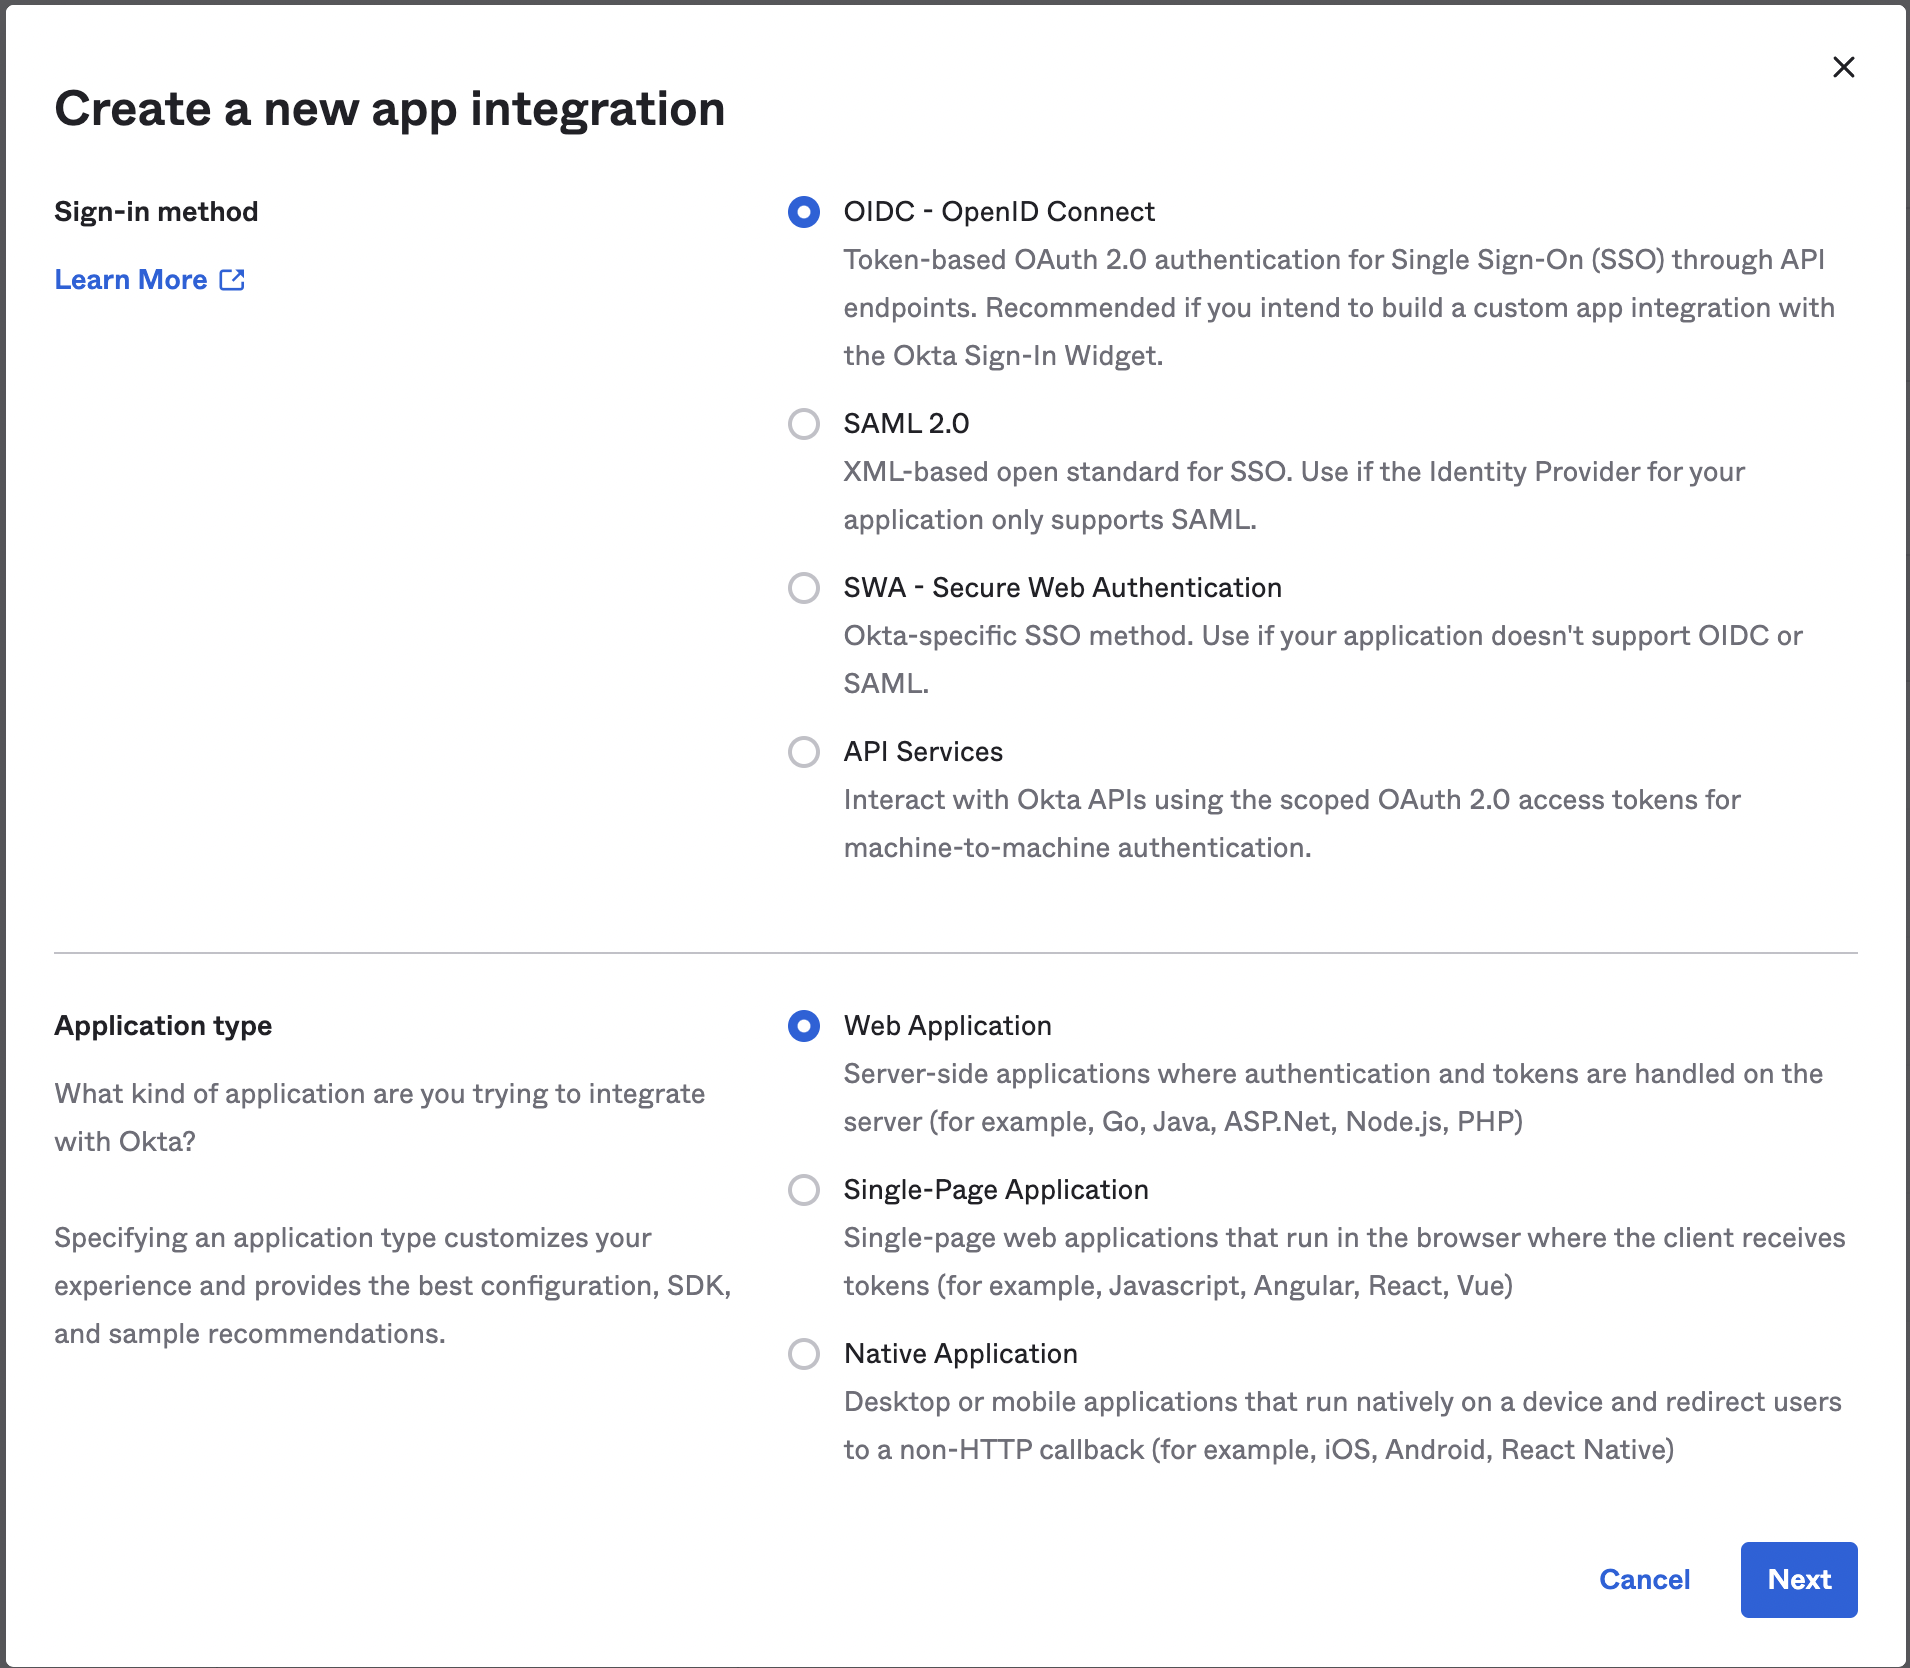
1. In Okta, select **Applications** > **Applications** > **Create App Integration** then choose **OICD OpenID Connect** and **Web Application.**
Create a new app integration in Okta
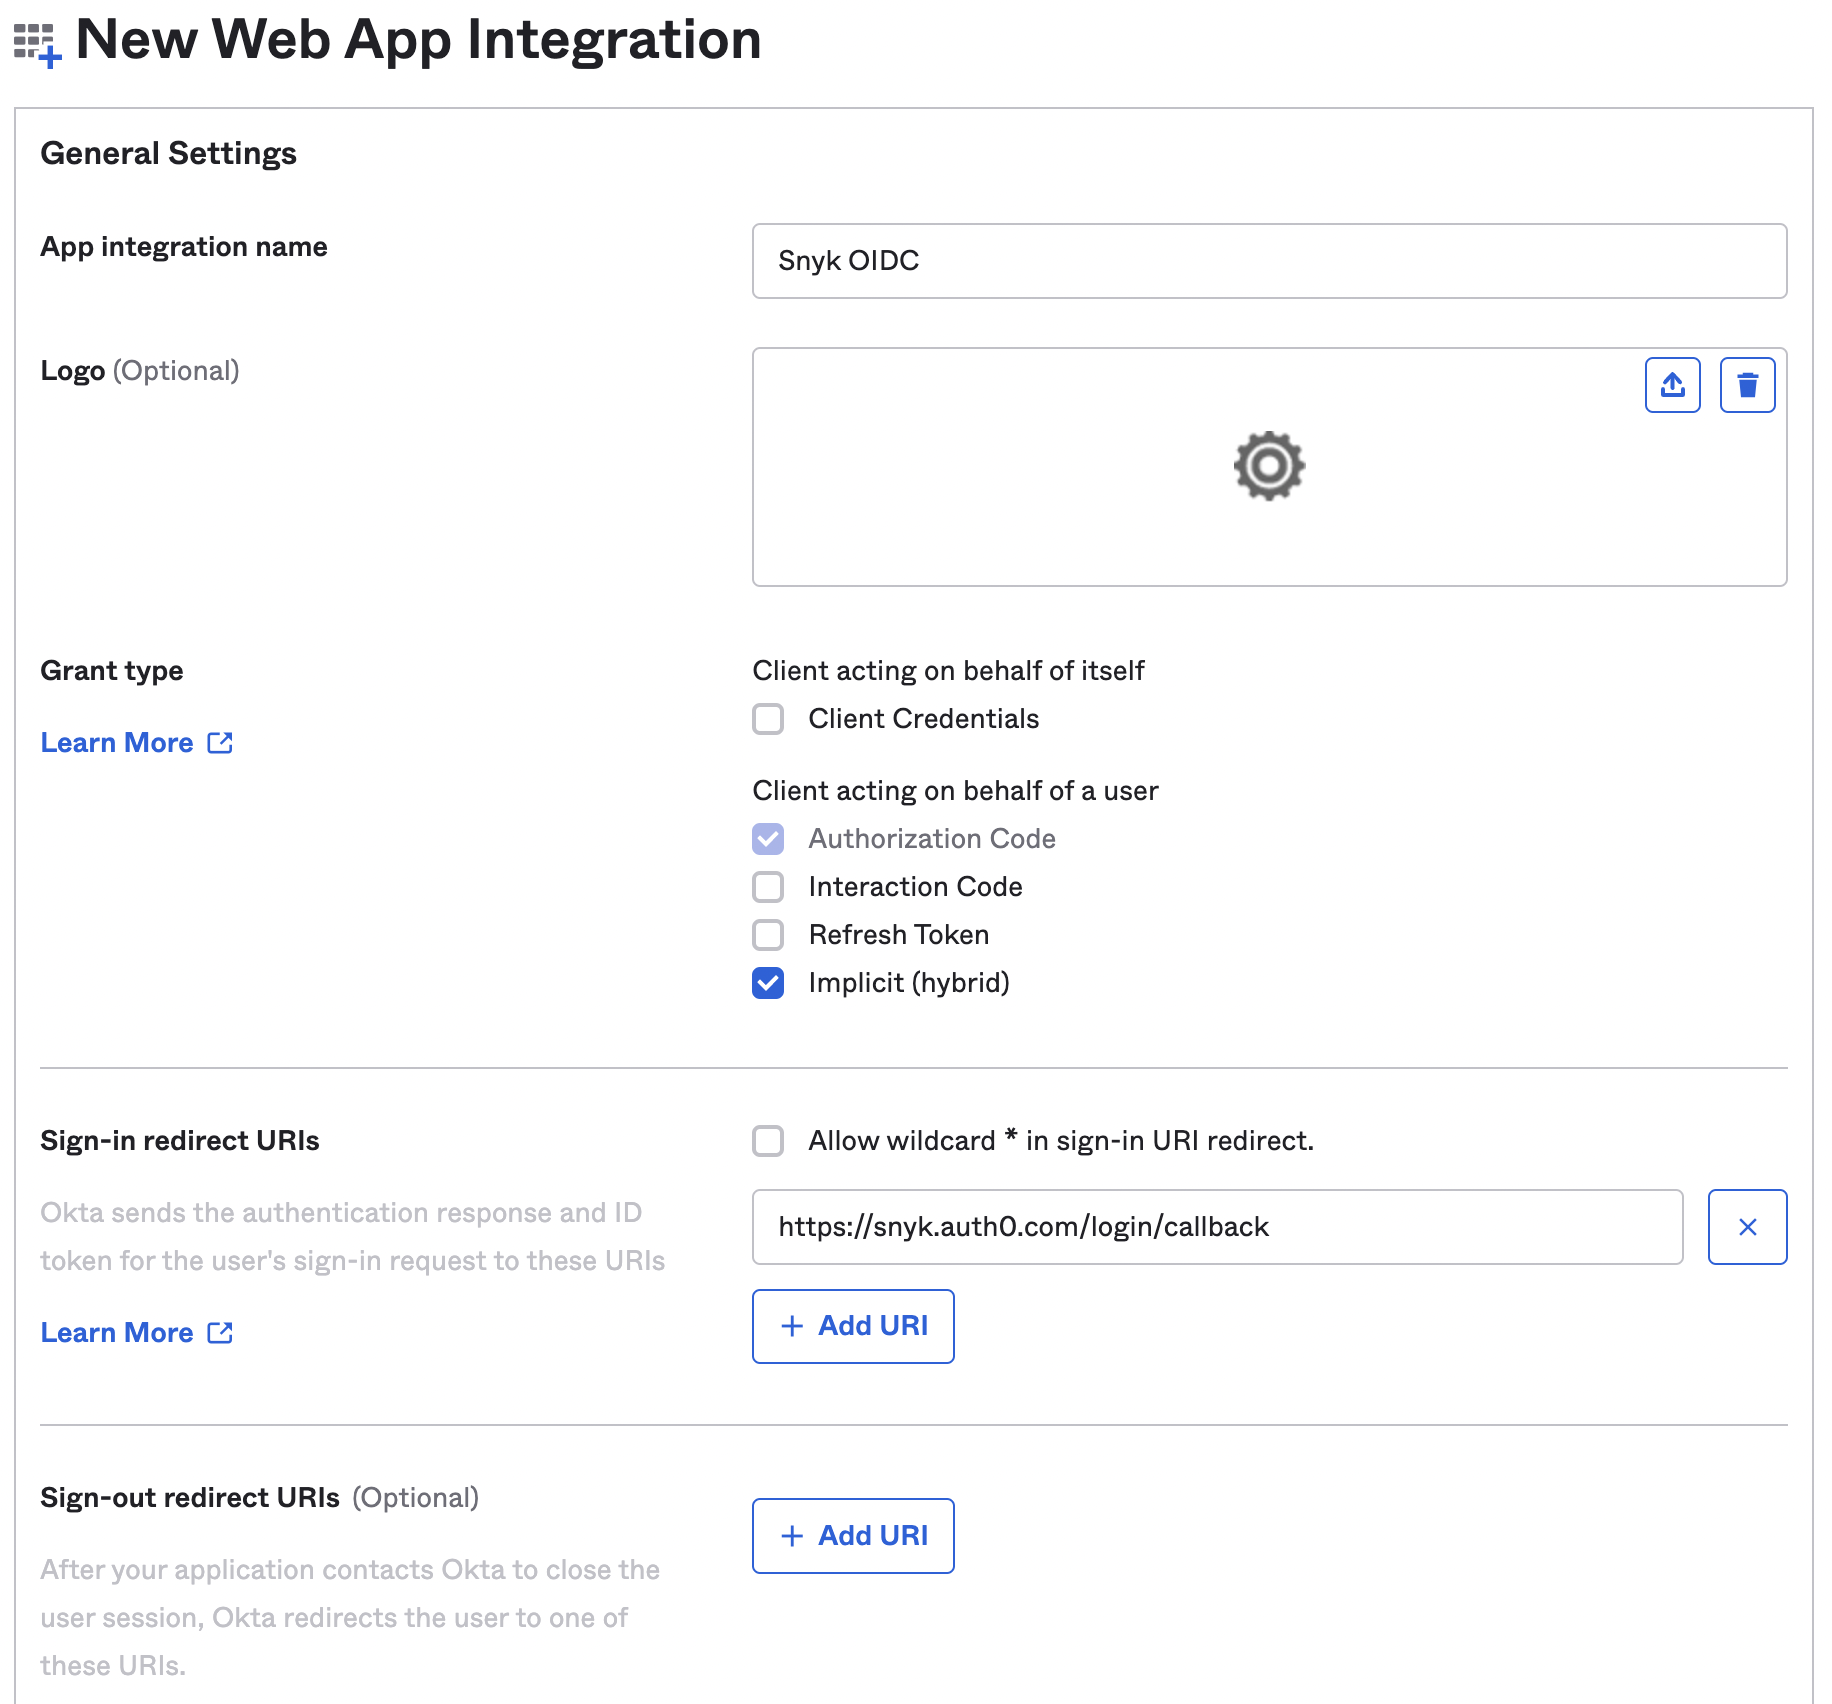
2. In the next step add an **App integration name** for your OIDC application, check the **Implicit** **Grant Type** and add the **Sign-in redirect URI** relevant to your [Snyk platform deployment](/platform-administration/user-management/single-sign-on-sso-for-authentication-to-snyk/set-up-snyk-single-sign-on-sso.md). Remove the placeholder **Sign-out redirect URI** and choose your assignment access control before clicking **Save.**
Provide details for new web app integration
3. On the application page that opens after saving, copy the details identified in [OIDC information to provide to Snyk](/platform-administration/user-management/single-sign-on-sso-for-authentication-to-snyk/set-up-snyk-single-sign-on-sso.md#oidc-information-to-provide-to-snyk) and provide to your Snyk contact:
* Client ID
* If you are not using the Implicit Grant type, the client secret
4. Also, share with Snyk the Issuer URL/domain. This is typically the URL you find in your browser address bar without "-admin", for example, . It can also be found under the **Sign-On** tab of your application by editing the **OpenID Connect ID Token** from **Dynamic** Issuer to **Okta URL**.
If you wish to set up custom mapping, move on to the next section of this guide.
### Add custom mapping
[Custom mapping](/platform-administration/user-management/single-sign-on-sso-for-authentication-to-snyk/custom-mapping.md) for an OIDC application in Okta is easily managed through custom attributes on the Group level.
#### Create a custom app user attribute to contain both the Snyk Organization name and role
1. In Okta, select your newly created OIDC application user profile under **Directory** > **Profile editor.**
2. Select **+Add Attribute.**
Okta profile editor
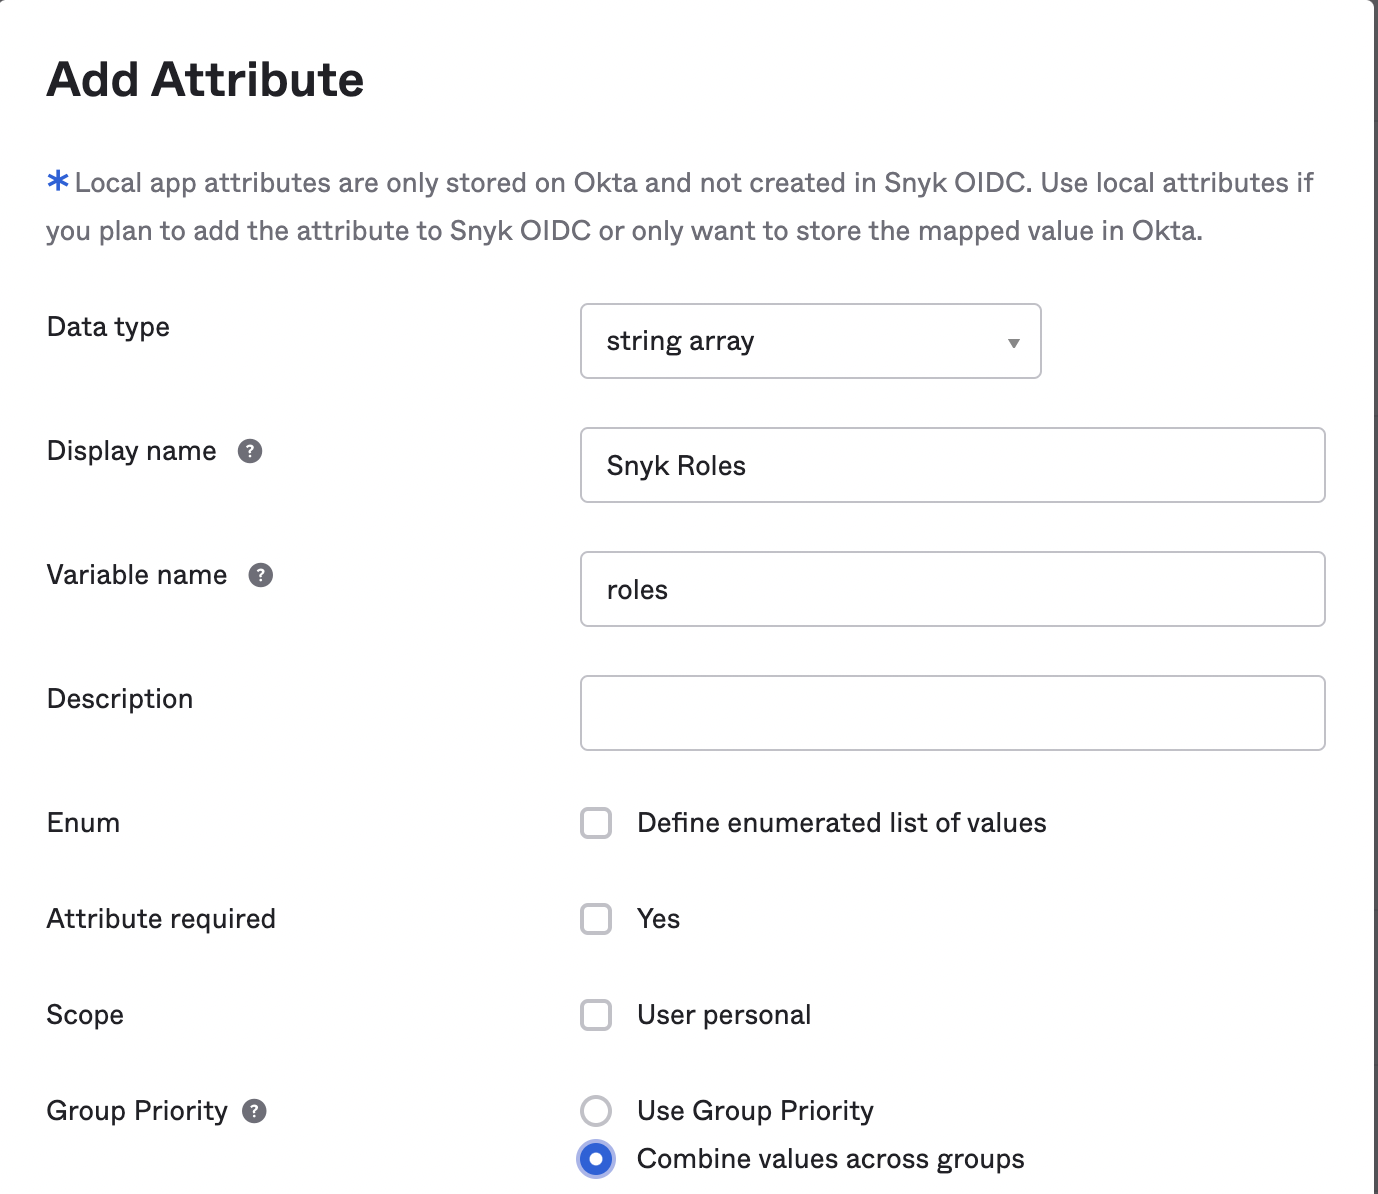
3. In the corresponding fields, add the following details for this Attribute and click **Save**:\
**Data type**: string array\
**Display name**: Snyk roles\
**Variable name:** roles\
**Group Priority**: Combine values across groups
Attribute details
#### Assign the attribute to the relevant Okta groups
1. On the main page of Okta select **Directory** > **Groups**.
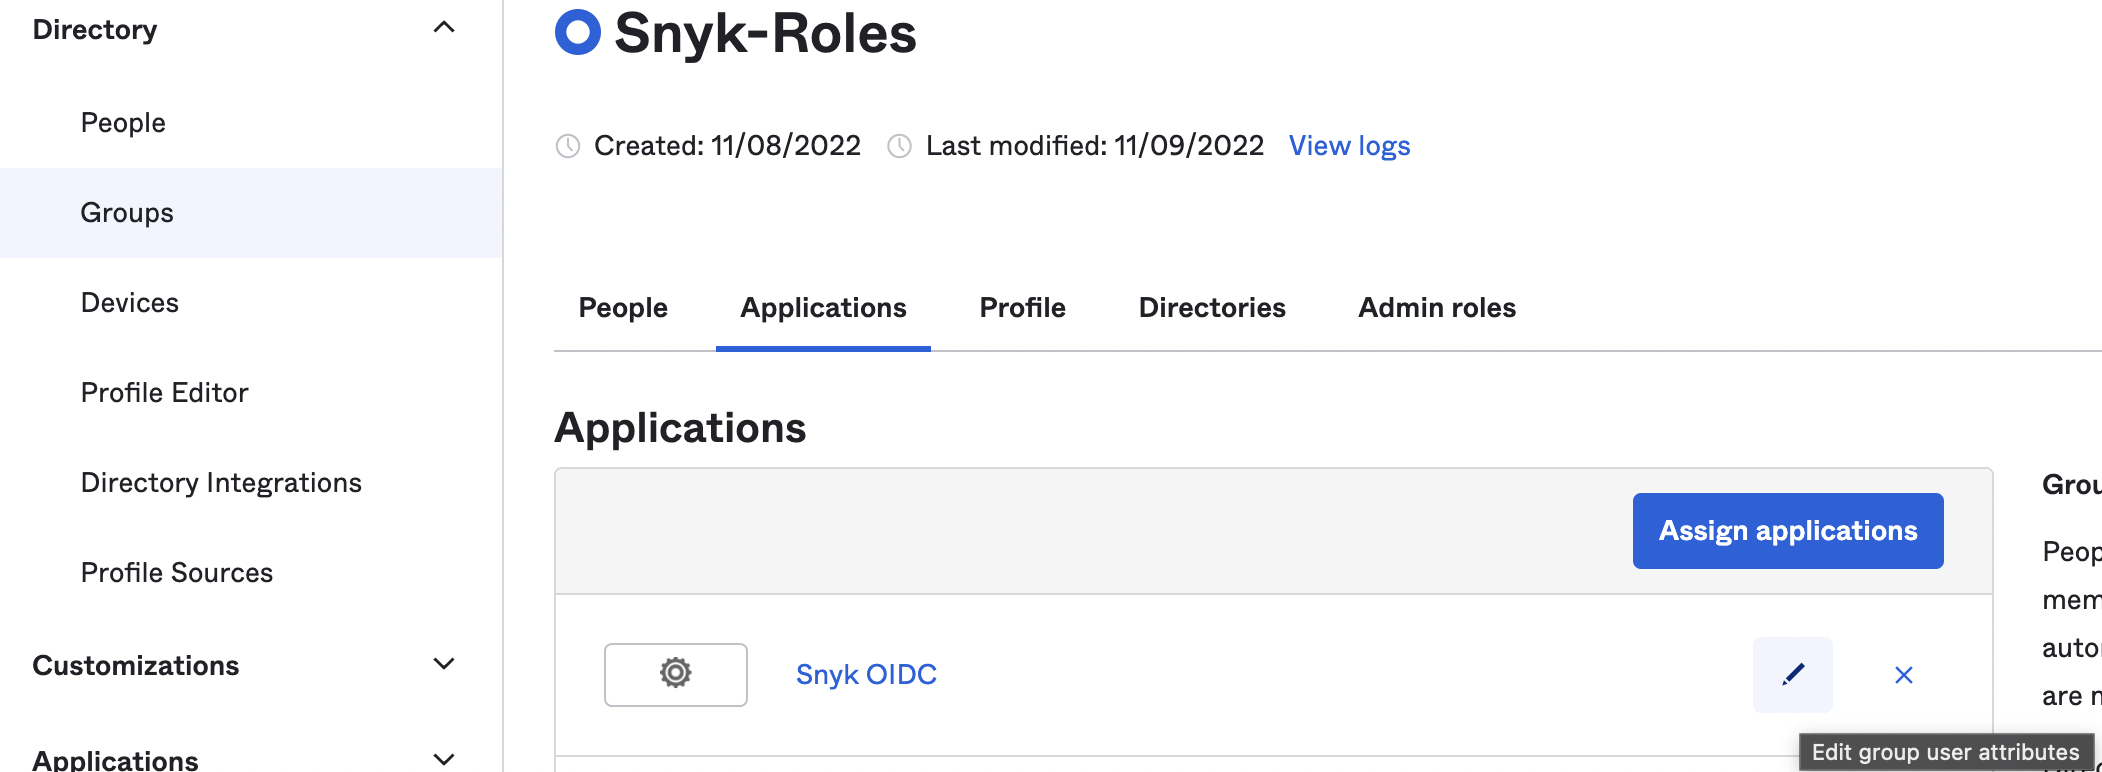
2. Select a **Group**, navigate to the **Applications** tab, click **Assign** **application** if not already assigned, and choose your Snyk OIDC app,. Then click on the pencil next to the displayed Snyk OIDC app.
Group selected for modicification
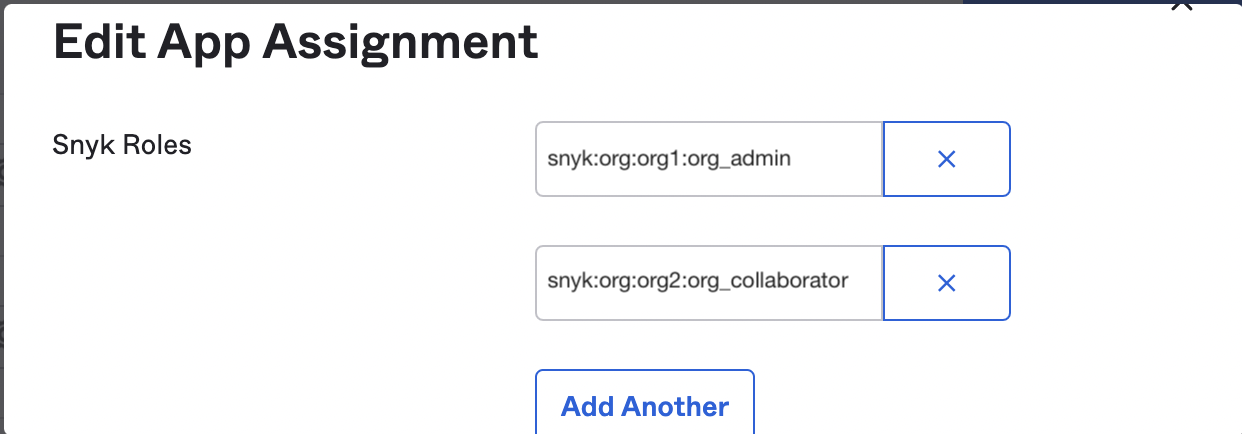
3. In the **Edit App Assignment** dialog, add the Snyk org name + role associated with your Okta group (no spaces or capital letter(s)), following the syntax explained in [custom mapping](/platform-administration/user-management/single-sign-on-sso-for-authentication-to-snyk/custom-mapping.md) (or [legacy custom mapping](/platform-administration/user-management/single-sign-on-sso-for-authentication-to-snyk/custom-mapping/legacy-custom-mapping.md) if using the legacy mapping option). Example, `snyk:org:*:org_admin`.\\
Adding Snyk roles
4. Repeat the preceding steps for all your applicable Okta groups to assign the org name and role combination to each user within each configured group.
Custom mapping is not active until Snyk turns it on for your Group. After Snyk confirms it is active, the mapping works when a user in a configured Okta group logs in and receives the roles in their `roles` attribute, at the scope and target each assertion names.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.snyk.io/platform-administration/user-management/single-sign-on-sso-for-authentication-to-snyk/custom-mapping/examples-setting-up-custom-mapping-for-idps/example-setting-up-custom-mapping-for-an-okta-oidc-app.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.